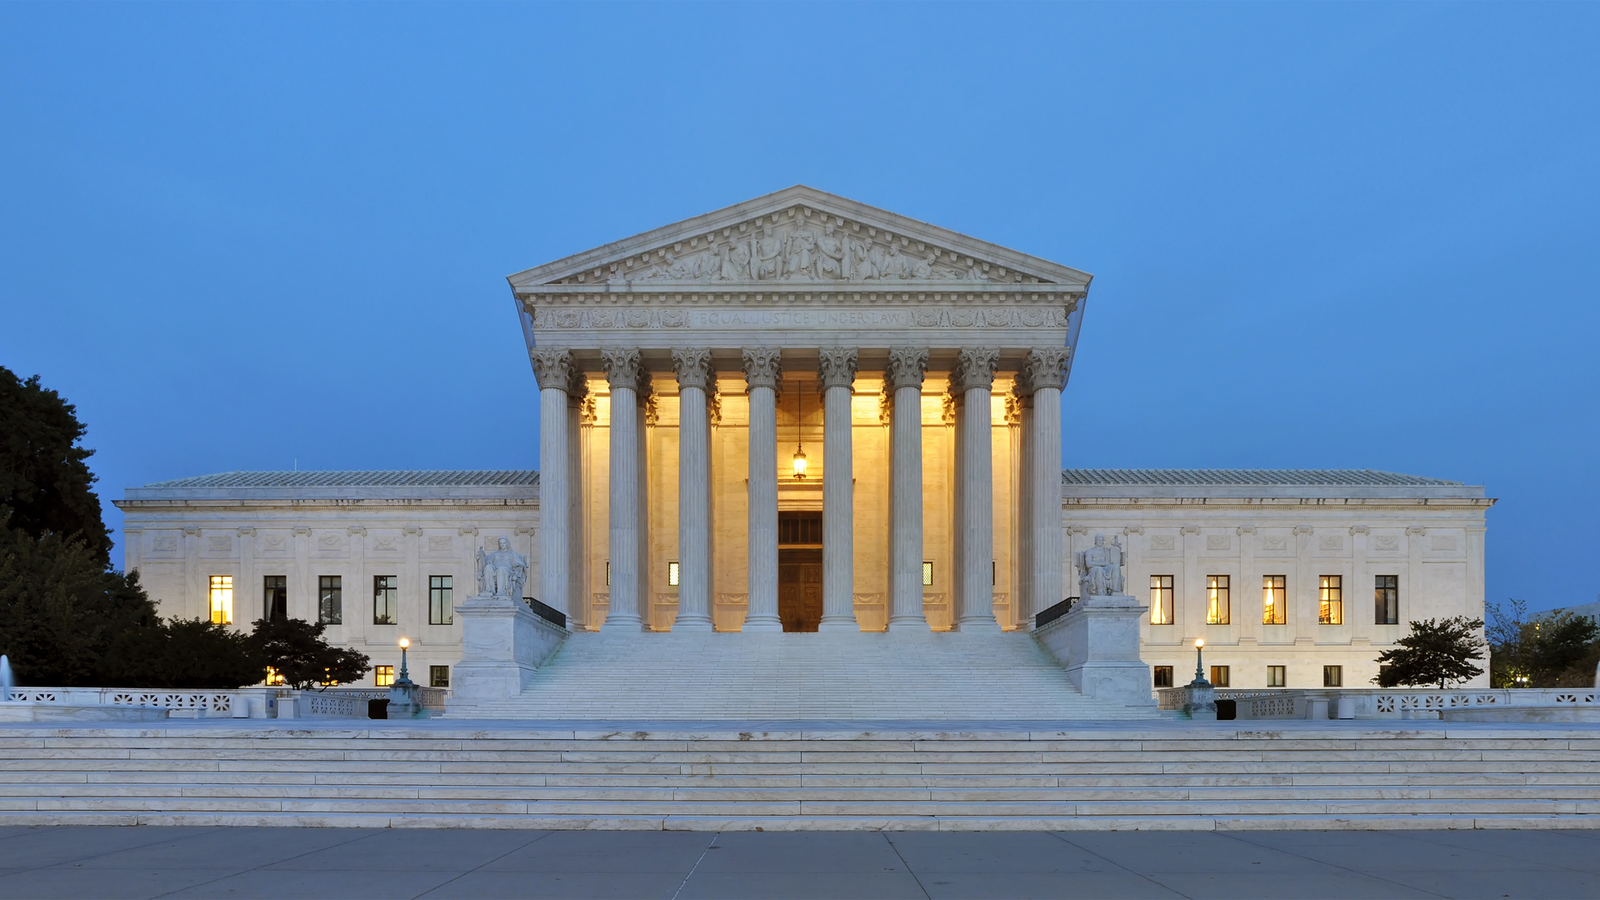
A quiet transparency rule is coming to a tool most people never see. TechCrunch reports U.S. courts will start publishing how often the government uses spyware. That is a shift from the current world, where mercenary-grade phone-hacking tools show up in classified or sealed paperwork and the public only hears about them after a leak, a lawsuit, or an Apple threat alert.
Why courts matter: a lot of this software is used with judicial process, or at least argued that way after the fact. If dockets begin to show frequency — even as counts, not target names — researchers, Congress, and vendors get a number instead of a rumor. It will not name every operation, and it will not stop spyware. It will make “we almost never use this” a claim you can check.
Pair this with Apple’s same-week threat notifications and you get a two-track week in device security: companies warning targets, and courts promising to tally use. For regular computer users the practical advice is unchanged — keep the OS current, treat unexpected lock-screen security alerts as real, and do not install random “device cleaners.” For the industry, published counts are the first step toward treating spyware like wiretaps: still used, but no longer invisible.